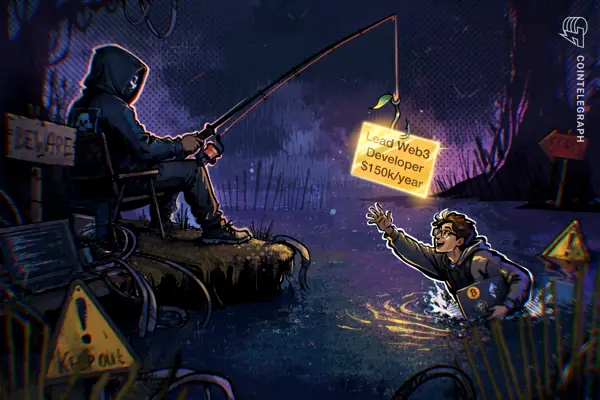
Months before the cryptocurrency exchange Binance suffered a staggering $6.3 billion cyberattack, its chief security officer had accurately described the exact tactic threat actors would use to breach the system. In an interview conducted in July, Binance Security Chief Jimmy Su highlighted how deceptive recruitment schemes and technical tests posed a severe internal threat to corporate security networks.
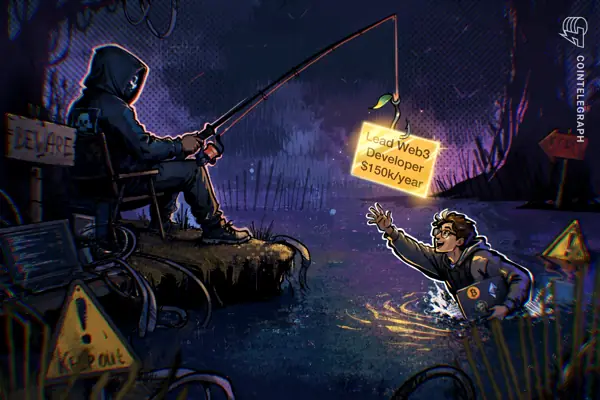
Su explained that malicious actors often tailor fake career opportunities to targeted employees, convincing them to run code as part of a technical hiring evaluation. Because these assessments frequently rely on routine developer actions—such as cloning a code repository from GitHub—traditional antivirus and endpoint protection tools often fail to flag the individual steps as malicious. Once executed, the obfuscated malware compromises the work computer, granting attackers access to extract credentials and move deeper into internal infrastructure.
This theoretical scenario materialized in September when a Binance software engineer downloaded a compromised coding assignment on a company laptop during a fraudulent job interview. The breach served as an entry point for a complex, multi-stage attack that culminated in the massive October theft. Su had previously emphasized that while staff members are free to explore outside employment opportunities, the burden lies on the organization to prevent execution and contain risks on company-owned devices within the crypto sector.
The incident has reshaped security protocols and hiring practices across the industry. Kevin Gibson of the recruitment agency Proof of Search noted that prospective employers now frequently ask whether candidates have been vetted in person to avoid falling victim to fraudulent job offers. Meanwhile, Binance reported blocking 57 cyber threats linked to North Korea this year alone—roughly one every five days. Following the breach, the company overhauled its internal wallet systems, tightened access controls, upgraded AI monitoring tools, increased endpoint security investments, and brought in third-party cybersecurity experts to review the breach.