Leading crypto-linked Visa debit card provider Gnosis Pay has announced a significant security incident, revealing that sensitive financial and personal information belonging to its customers was compromised.
The breach, which was detected on November 3, involved unauthorized access to the company's legacy consumer card system.
Gnosis Pay swiftly responded, initiating containment measures within two hours of discovery.
The firm has assured its user base that despite the exposure of data, customer funds remain secure and its separate enterprise platform, which facilitates various white-label card programs, was unaffected by the intrusion.
An analysis of breach notifications, independently reviewed by Cointelegraph, confirmed the extensive nature of the exposed data.
This included complete payment card numbers, their corresponding expiration dates, and CVV codes.
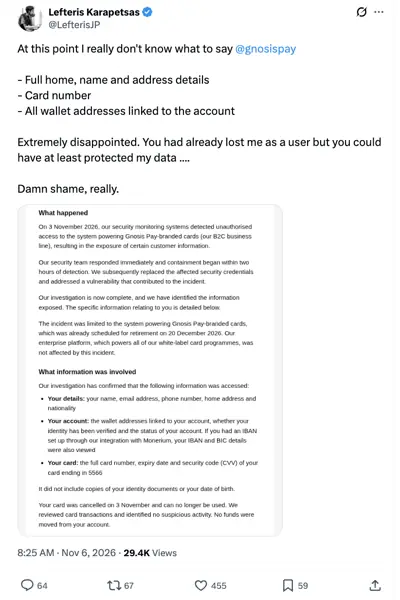
Beyond payment specifics, the compromised information also encompassed a broad spectrum of personal identifiers such as customer names, home addresses, email addresses, phone numbers, and nationalities.
Crucially for users in the digital asset sector, cryptocurrency wallet addresses linked to the affected accounts were also part of the exposed dataset.
In certain instances, banking details, including IBAN and BIC information, were also compromised.
A specific notification shared by customer Lefteris Karapetsas highlighted the cancellation of their card on November 3, with no suspicious transactions or fund movements reported, reinforcing Gnosis Pay's claims about fund safety.
In response to the security lapse, Gnosis Pay has implemented several corrective actions.
The company stated it has replaced all compromised security credentials and successfully addressed the underlying vulnerability that led to the breach.
Furthermore, to enhance immediate security for online transactions, Gnosis Pay has made 3D Secure verification mandatory.
This requirement will remain in effect until the legacy system, the point of entry for the breach, is scheduled for retirement on December 20.
The firm also issued a warning to its customers regarding potential phishing attempts that could leverage the stolen personal or transaction details.
As part of its commitment to mitigate risk, Gnosis Pay is reportedly arranging monitoring services to detect and address any potential misuse of the stolen customer data.
Despite these assurances and mitigation efforts, Gnosis Pay has not yet publicly disclosed the total number of customers impacted by the breach.
The company also did not immediately respond to a request for comment from Cointelegraph regarding the incident.
Third-party data from OpenRate, a platform that tracks activity within the crypto card market, indicates that Gnosis Pay typically serves around 2,400 daily active cardholders, processing approximately $263,200 in transactions over a 24-hour period prior to the disclosure.
This incident underscores the ongoing security challenges faced by companies operating at the intersection of traditional finance and the rapidly evolving cryptocurrency landscape.